Fortinet Hybrid Mesh Firewall
One firewall policy across the data centre, the branch and the cloud — enforced by whichever FortiGate form factor fits each place, and managed from a single console. Grizzly X is a Canadian reseller — tell us where the sites are and we will scope it.
One policy, four form factors, one console
A hybrid mesh firewall is not a product you buy. It is an architecture: the same security policy enforced at every point traffic enters or leaves your estate, no matter whether that point is a rack in a colocation facility, a branch closet, a virtual machine or a cloud VPC.
Gartner coined the term because the old model stopped working. Estates grew a perimeter in the data centre, another in each branch, another in every cloud account, and each one was configured by hand in its own console. The gaps between them are where incidents start.
Fortinet's answer is to run one operating system, FortiOS, on every form factor, and manage the whole mesh from FortiManager with FortiAnalyzer for the telemetry. A rule written once applies everywhere it should.
Hybrid Mesh Firewall: The Next Evolution of Firewalls
The four enforcement points
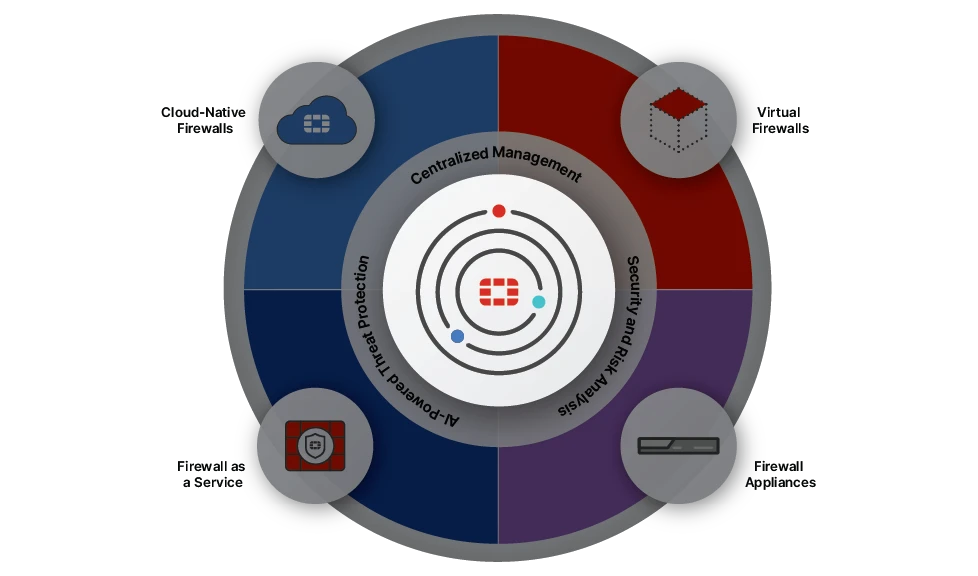
Each of these is a FortiGate. They differ in how they are delivered, not in what policy they run.
-
Firewall appliances
Purpose-built hardware with Fortinet's own security processors. The SPUs offload inspection from the CPU, which is why a desktop FortiGate can run full threat protection on a branch link without becoming the bottleneck. This is the right choice wherever traffic is heavy, predictable and physical.
-
Virtual firewalls
FortiGate-VM, the same FortiOS running on VMware, Hyper-V, KVM, Nutanix or Proxmox. Use it where you already have compute and want east-west segmentation inside the data centre without another rack unit.
-
Cloud-native firewalls
FortiGate deployed from the AWS, Azure or Google Cloud marketplaces, inside the VPC or VNet it protects. Policy comes from the same FortiManager as the hardware, so a cloud workload is not an exception to your rules.
-
Firewall as a service
FortiSASE, where Fortinet runs the enforcement point and you consume it. The fit is remote and roaming users who never touch an office, and sites too small to justify hardware.
What holds the mesh together
-
Centralized management
FortiManager pushes policy, firmware and configuration to every FortiGate in the estate, physical or not. Change control, templates and role-based access live here, which is what turns a hundred firewalls into one system.
-
AI-powered threat protection
FortiGuard services feed every enforcement point the same intelligence — IPS signatures, web filtering, antivirus, botnet and DNS categories — updated continuously rather than per-device.
-
Security and risk analysis
FortiAnalyzer collects logs from the whole mesh and reports across it: what was blocked, where a policy is too loose, which devices drifted from the template, and what a given user actually did.
Where it earns its keep
Data centre segmentation
East-west traffic between workloads is the part most estates never inspected. A FortiGate at the core — appliance or VM — applies zero-trust segmentation between zones, so a compromised host cannot simply walk sideways. Throughput is the constraint to design around, which is where the higher-end appliances and their SPUs matter.
Securing Your Data Center with FortiGate Network Firewalls
Branch connectivity
A branch FortiGate is a firewall, an SD-WAN edge and a LAN and Wi-Fi controller in one box. Fewer devices on site means fewer things to fail and fewer consoles to reconcile, and the branch inherits the same policy as everywhere else rather than a local approximation of it.
Simplify Your Network and Security with Fortinet Secure SD-WAN
Cloud and multi-cloud
Workloads in AWS, Azure and Google Cloud get the same inspection and the same rules as the on-premises estate, without hand-translating policy into each provider's native security groups. Visibility of what those workloads are actually doing comes back to the same FortiAnalyzer.
One console, not twelve
The reason the mesh works is the management plane. FortiManager holds the policy packages and templates; FortiAnalyzer holds the logs and the reporting; both see every enforcement point regardless of form factor.
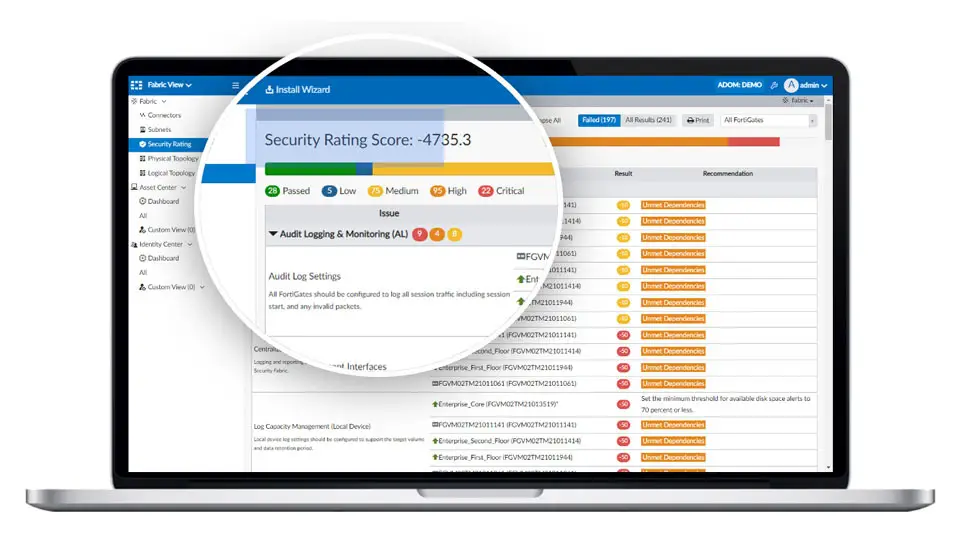
The practical payoff is the security rating: a running score of how far the estate has drifted from good practice, with the specific devices and settings named. It is the difference between believing your firewalls are configured correctly and being able to show it at audit.
Analyst position
Fortinet was named a Leader in the 2026 Gartner Magic Quadrant for Hybrid Mesh Firewall, and placed highest in Ability to Execute for the second consecutive year.
Gartner, Magic Quadrant for Hybrid Mesh Firewall, Rajpreet Kaur, Adam Hils, Odie Adesina, 7 September 2026.
GARTNER is a registered trademark and service mark of Gartner, Inc. and/or its affiliates in the U.S. and internationally, and MAGIC QUADRANT is a registered trademark of Gartner, Inc. and/or its affiliates, and are used herein with permission. All rights reserved. Gartner does not endorse any vendor, product or service depicted in its research publications, and does not advise technology users to select only those vendors with the highest ratings or other designation. Gartner research publications consist of the opinions of Gartner's research organization and should not be construed as statements of fact. Gartner disclaims all warranties, expressed or implied, with respect to this research, including any warranties of merchantability or fitness for a particular purpose.
Common questions
What is a hybrid mesh firewall?
A hybrid mesh firewall is a security architecture in which several firewall form factors — hardware appliances, virtual machines, cloud-native instances and firewall-as-a-service — enforce one shared policy and are managed from a single console. Gartner introduced the category to describe estates that no longer have a single perimeter to defend.
How is it different from a next-generation firewall?
A next-generation firewall is one enforcement point. A hybrid mesh firewall is many of them, of different kinds, under one policy and one management plane. With Fortinet the enforcement points are FortiGate NGFWs, so you are not replacing the NGFW — you are tying several together.
Do I have to replace my existing FortiGates?
No. Any FortiGate running a current FortiOS release can be brought under FortiManager, including hardware already deployed. The usual first step is to adopt the existing estate into central management and see the security rating before buying anything.
Can I mix hardware, virtual and cloud firewalls?
That is the point of the architecture. All four form factors run the same FortiOS and take policy from the same FortiManager, so the decision at each site is about throughput, physical constraints and licensing, not about which policy it will run.
Do I need FortiManager and FortiAnalyzer?
For a handful of firewalls, no. The threshold is usually somewhere around ten devices or the first compliance audit, whichever arrives first. Below that, FortiGate's own interface and cloud logging are generally enough; above it, the hand-configuration becomes the risk.
Does Grizzly X supply this in Canada?
Yes. We are a Canadian Fortinet reseller, supplying the appliances, FortiGate-VM licences, FortiManager, FortiAnalyzer and the FortiGuard subscriptions that go with them. Coverage varies by province, so tell us where the sites are along with the throughput you need and we will confirm what we can deliver and quote it.
Scoping a hybrid mesh firewall?
Tell us how many sites, what throughput each one needs and where the workloads live. We will come back with the FortiGate models, licences and management pieces that fit — and what we would leave out.
Request a Quote