Desktop
TZ80
The subscription-based entry model: 750 Mbps across every inspection engine in a palm-sized box, for a home office, a micro-site or an IoT segment.
SonicOS750 Mbps firewall750 Mbps threat preventionSubscription-based
Desktop next-generation firewalls for branch offices, retail sites and small businesses, from 2.5 to 5 Gbps of inspected throughput.
The subscription-based entry model: 750 Mbps across every inspection engine in a palm-sized box, for a home office, a micro-site or an IoT segment.
The entry point to Gen 8: 2.5 Gbps of firewall inspection and eight gigabit ports in a fanless desktop unit.
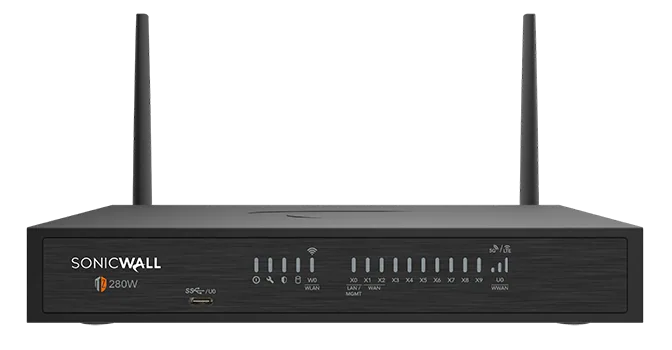
The TZ280 with a 2x2 802.11ax radio built in, for a site that needs wireless without a separate access point.
The TZ280 with four PoE+ ports and a 120 W budget, so phones, cameras and access points run off the firewall.
3.5 Gbps of firewall inspection and two 5G/2.5G SFP+ uplinks, for a branch outgrowing gigabit.
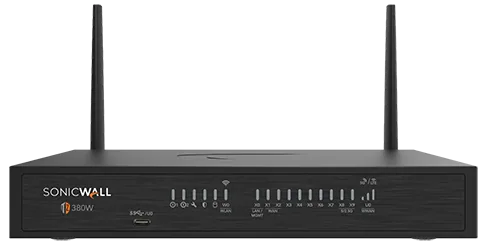
The TZ380 with a 2x2 802.11ax radio built in, keeping the 5G/2.5G SFP+ uplinks.
4 Gbps of firewall inspection, 2,500 SAML users and 32 managed access points.
4.5 Gbps of firewall inspection, 500,000 DPI connections and 250 site-to-site tunnels.
The top of the Gen 8 TZ range: 5 Gbps of firewall inspection and two 10G SFP uplinks.
Each model set against the next one up the range, specification by specification.
A TZ gives a branch enterprise-grade security without enterprise-grade complexity or cost.
Every packet is inspected at full speed, encrypted traffic included. Malicious content is stopped before it reaches a user rather than reported after it arrives.
Unknown files are detonated in a cloud sandbox before delivery, so malware that no signature has seen yet still has nowhere to hide.
Signatures for intrusion prevention, anti-malware, botnet filtering and content filtering refresh automatically from the Capture Cloud Platform as part of the security services. There is nothing to apply by hand.
With Cloud Secure Edge integrated, the same protection follows a user on site, at home and in the cloud, so there is no gap between the three.
Firewall, SD-WAN, ZTNA, content filtering, sandboxing, Cloud Secure Edge and managed services in place of a stack of separate tools.
Policies, analytics, compliance reports and user access across every firewall in the organisation, from a single dashboard rather than one console per site.
Built-in failover and performance that scales from a branch TZ to a data-centre NSsp, with the same management model the whole way up the range.
The essential services arrive bundled rather than bought, integrated and maintained separately, which takes a layer of licensing and operational overhead out of the picture.
The Managed Protection Security Suite puts SonicWall's SonicSentry team on the firewall itself: monitoring, response, policy tuning, firmware updates and monthly health checks.
Tell us the user count, the uplink speed and whether the site needs Wi-Fi or PoE built in. We will confirm the model, the licence term and the lead time, then quote it.
Request a Quote